CIS Benchmark gaps
Default Kubernetes installs fail most CIS benchmarks. We baseline clusters with Pod Security Standards, RBAC least-privilege and network policies before the first workload deploys.
Twenty-three production Kubernetes clusters managed — ANT's PropTech marketplace on EKS with Karpenter, LiMP's consumer VPN on a hardened cluster, ArgoView's clinical workstation on an AKS cluster compliant with HealthTech controls. GitOps with Argo CD, Cilium network policies, Falco runtime protection and PITR backup from day one.
We deliver Kubernetes engineering for product teams scaling past single-server deployments, regulated industries requiring network-policy isolation and audit-grade access controls, multi-tenant SaaS platforms needing namespace or vCluster isolation, and organisations migrating from Docker Compose or Nomad. EKS, AKS and GKE are all in production for us. Argo CD handles GitOps deployments. Karpenter handles cost-efficient node scaling. Falco and Trivy handle runtime security.
Default Kubernetes installs fail most CIS benchmarks. We baseline clusters with Pod Security Standards, RBAC least-privilege and network policies before the first workload deploys.
StatefulSets with dynamic PVC provisioning across AZs require careful storage class design. We configure topology-aware provisioning and PodDisruptionBudgets for safe rolling updates.
Default CPU-based HPA reacts too slowly to event-driven spikes. We wire KEDA with queue-depth metrics for sub-minute scale-out.
Rotating secrets across clusters manually introduces drift and outages. We centralise on External Secrets Operator pulling from a single secrets backend.
In-place upgrades on production clusters cause kubelet restarts and potential pod evictions. We use blue-green cluster upgrades for stateless workloads and test upgrades in staging first.
Pod resource requests and limits set too high waste node capacity. We implement OpenCost for per-namespace cost allocation and Goldilocks for VPA recommendations.
Production-ready EKS/AKS/GKE with Karpenter, Argo CD, Cilium, Prometheus stack, Falco and CIS Benchmark baseline — in two weeks.
Pod Security Standards, network policies, RBAC audit, Trivy CI scanning, Falco runtime rules and CIS Benchmark remediation.
Migration from kubectl apply or Helm CI scripts to Argo CD ApplicationSets — full GitOps with rollback, sync status and Slack alerts.
Namespace RBAC, network isolation and vCluster virtual clusters for SaaS platforms with strict tenant separation requirements.
OpenCost per-namespace cost reports, Karpenter spot consolidation, Goldilocks VPA recommendations and cluster bin-packing audits.
Blue-green cluster upgrades, namespace migration playbooks and version-upgrade path documentation with rollback procedures.
GDPR-aligned · SOC 2-capable · HIPAA-eligible · PCI DSS-aware
Shared: CIS Kubernetes Benchmark, SBOM via Trivy SBOM, SLSA supply-chain controls.
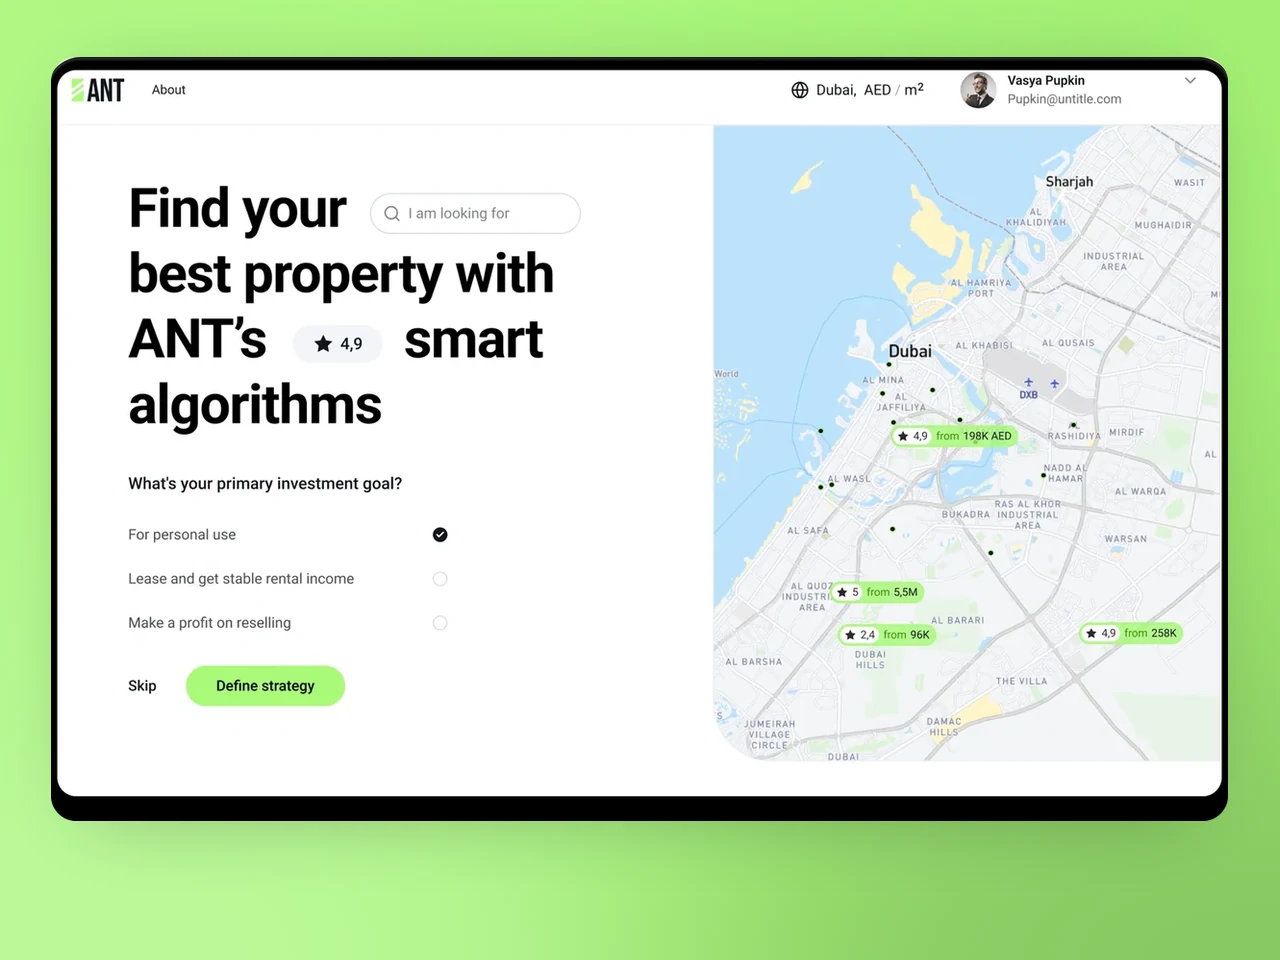
Property marketplace web platform with listing CMS, search and B2B admin console for US and EU operators.
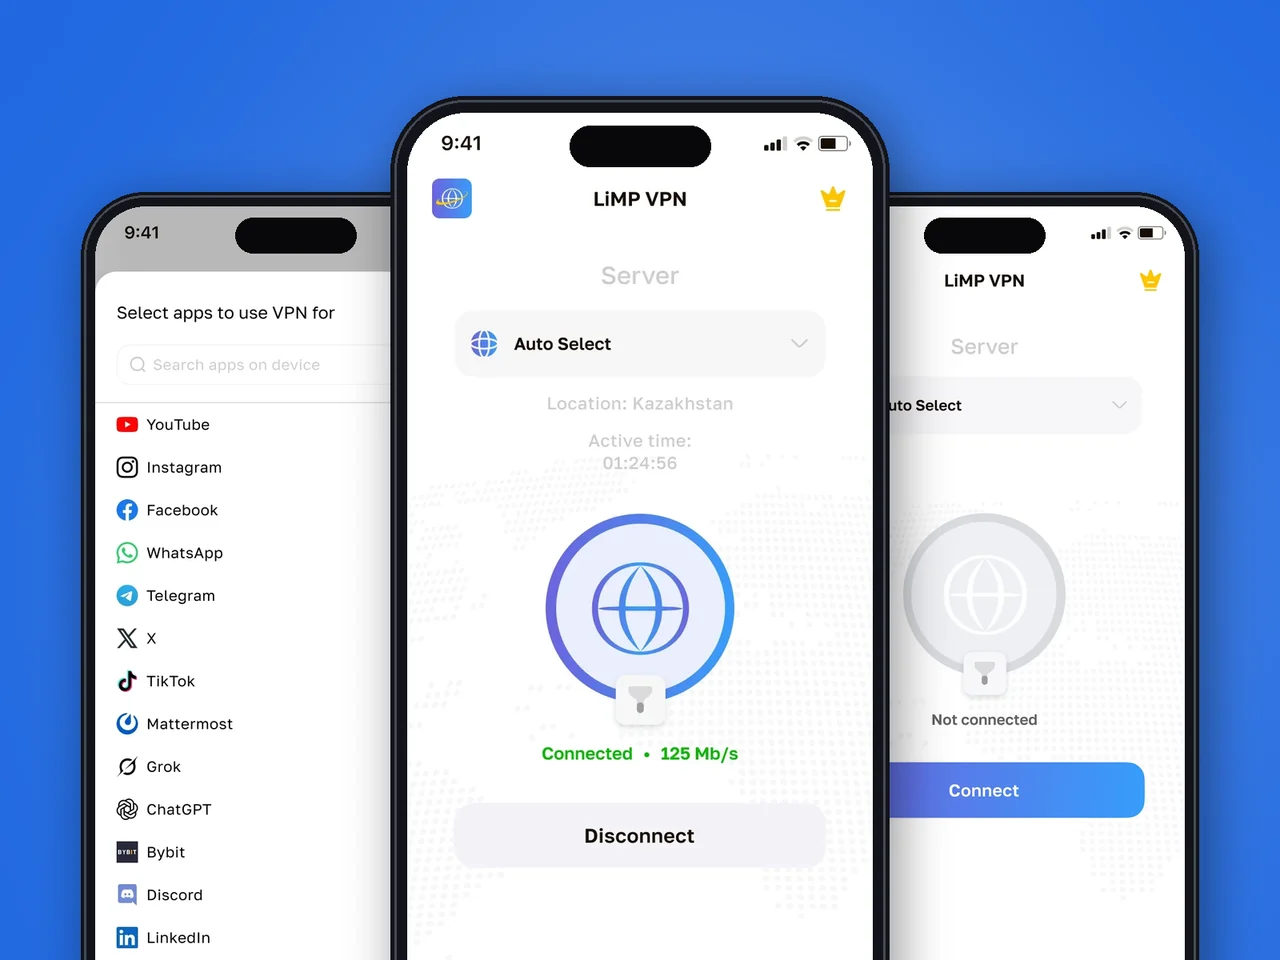
Consumer WireGuard VPN app for iOS and Android with zero-log architecture, launched across the US and EU.
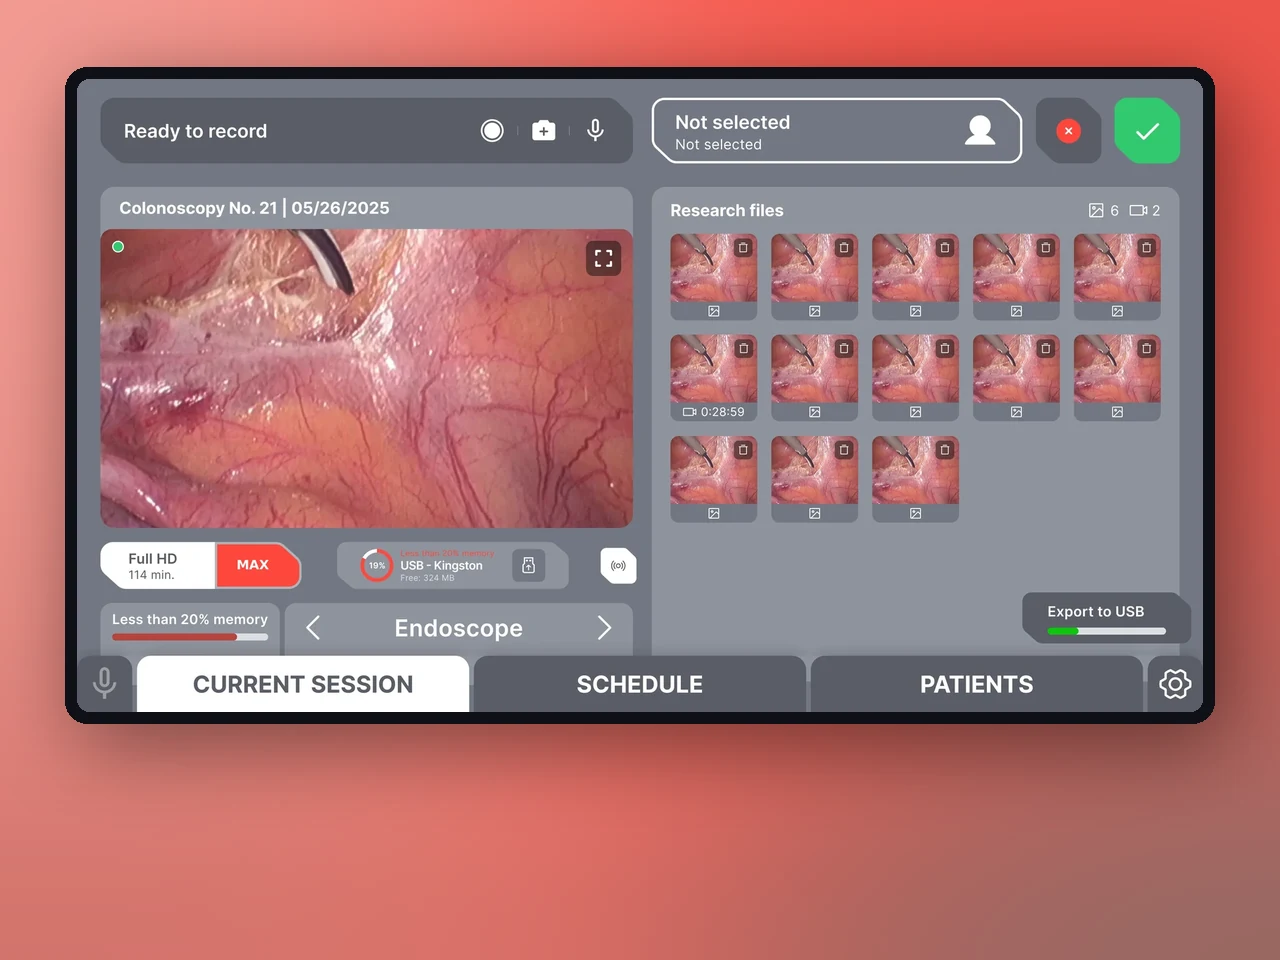
Tablet-first endoscopy recording, patient records, and DICOM/HL7 export — built on Laravel + React with browser-tier WebRTC capture for US & EU clinics.
Privacy apps live and die by trust. YuSMP built a no-logs WireGuard implementation with a server latency map, one-tap connect, and kill switch — every feature we had promised users. Apple review approved on the first submission.
Clinical workflow software that hospitals actually adopt is rare. YuSMP built an iPad-first endoscopy platform with HD video capture, DICOM export, and HL7 integration. Medical staff needed almost no training because the UX is genuinely intuitive.
A loan decision engine that takes ten times less time to approve does not happen by accident. YuSMP built the scoring pipeline, integration with credit bureaus, and a back-office that our underwriters actually enjoy using. Approval turnaround went from two days to under four hours.
We publish dozens of sports articles a day. YuSMP built an editorial pipeline using a Telegram bot as the CMS — editors post once, content lands on web, iOS, and Android instantly. The architecture requires zero daily maintenance.
1 / 4
We do not ship Kubernetes clusters without a CIS Benchmark baseline. Pod Security Standards, network policies and RBAC least-privilege are part of the initial cluster setup, not a post-audit retrofit.
OpenCost per-namespace cost reports, Karpenter spot consolidation and Goldilocks VPA recommendations — cost visibility from the first sprint.
No human touches production with kubectl apply. Argo CD ApplicationSets, diff previews and one-click rollback — every change is a Git commit with a review.
FAQ
EKS if your primary cloud is AWS — best IAM integration with IRSA, widest tooling ecosystem. AKS for Azure-centric organisations with Entra ID (AAD) integration requirements. GKE Autopilot for teams wanting the most hands-off cluster management experience. We design cloud-agnostic workloads where portability is a stated requirement.
Argo CD is our default — UI, ApplicationSets, app-of-apps pattern, RBAC and Slack notifications. Flux where teams have an existing Flux investment or a strong preference for its GitOps operator model. Both tools achieve the same outcome; the choice rarely matters more than consistency.
External Secrets Operator pulling from AWS Secrets Manager, Azure Key Vault or HashiCorp Vault — never secrets in Git, even encrypted. We also implement Sealed Secrets for teams that want Git-stored encrypted secrets without a cloud secrets backend dependency.
We baseline every cluster against CIS Kubernetes Benchmark: Pod Security Standards, network policies (Cilium), RBAC least-privilege, audit logging, Falco runtime threat detection and Trivy image scanning in CI. Cluster security findings are tracked in the same sprint as feature work.
HPA on custom metrics (KEDA event-driven) for queue consumers, combined with Karpenter for node-level scale-out. We model the cold-start latency budget and choose between over-provisioning (fast response) and zero-to-burst (cost-efficient) based on your SLA.
Namespace-per-tenant with network policies and RBAC for moderate isolation. vCluster virtual clusters for teams requiring stronger API-server isolation without the cost of dedicated clusters. Dedicated clusters for regulated tenants where the compliance boundary must be a cluster.
Blue-green cluster upgrades for stateless workloads — new cluster, migrate namespaces, drain old. Rolling node upgrades with PodDisruptionBudgets for stateful workloads. We test the upgrade path in staging with production-equivalent loads before touching production.
Tell us where you want to be in twelve months. We’ll come back with a plan to get you there.
Response within 1 business day. NDA on request.
Share a few details and a senior consultant will reply within one business day.
Email: sales@yusmpgroup.com
Phone: +374 44 871 811
Offices: KAMAR Business Center, Vazgen Sargsyan St. 2, Yerevan, Armenia · Remote — East-Coast US overlap (9 AM–1 PM ET)