any epidemic in legacy bases
Implicit any from JS migration and explicit any shortcuts accumulate until the type system provides no safety. We track any count per module and require it to decrease per PR.
Every greenfield project at YuSMP defaults to strict TypeScript across front and back. We pair Zod at API boundaries, generate types from OpenAPI specs, enforce type coverage as a CI gate, and run tsc --noEmit as part of every PR check. Thirty-plus production systems — Signatory Pro's e-signature platform, ArgoView's clinical workstation, ANT's PropTech marketplace — all type-safe end-to-end.
We deliver TypeScript engineering for SaaS and fintech teams migrating JavaScript codebases to strict TypeScript, product teams building new end-to-end typed stacks with React, Next.js and NestJS, platform teams designing monorepo type-sharing infrastructure, and regulated industries where type safety at API boundaries is a risk-reduction requirement. Type coverage is a CI gate, not a code review suggestion.
any epidemic in legacy basesImplicit any from JS migration and explicit any shortcuts accumulate until the type system provides no safety. We track any count per module and require it to decrease per PR.
Frontend types diverging from backend responses produce runtime crashes that TypeScript cannot catch. We generate frontend types from OpenAPI specs or use tRPC for zero-divergence contracts.
TypeScript build times on large codebases exceed 10 minutes without project references. We configure tsconfig references for incremental builds and add remote cache via Turborepo.
Third-party @types packages lag behind library versions, causing compile errors after upgrades. We pin @types versions alongside library versions and review them together.
Overengineered generics produce error messages no one can parse and types no one can understand. We prefer readable inferred types over explicit generics where the inference is obvious.
TypeScript only validates at compile time — network payloads, environment variables and config files are unknown at runtime. We add Zod validation at all system boundaries.
Incremental enabling of strict TypeScript on JavaScript or loose TS codebases — with type-coverage tracking and a PR ratchet that prevents regression.
Turborepo or Nx monorepos with shared types packages, project references for incremental builds and eslint-plugin-import boundary enforcement.
OpenAPI spec-first development with orval or openapi-typescript generating typed API clients — updated automatically on spec change.
Full-stack TypeScript with tRPC — no API client generation, instant type propagation from backend router to frontend query hook.
Runtime validation at all system boundaries — HTTP request bodies, environment variables, config files, LLM structured outputs — with TypeScript inference from schema.
ESLint rules for no-explicit-any, no-non-null-assertion, type-coverage thresholds and import constraints — enforced in CI, not just style guides.
GDPR-aligned · WCAG 2.2 AA · SOC 2-capable · HIPAA-capable · CCPA-acknowledged
Shared: OWASP ASVS L2, typed input validation with Zod, SBOM per build.
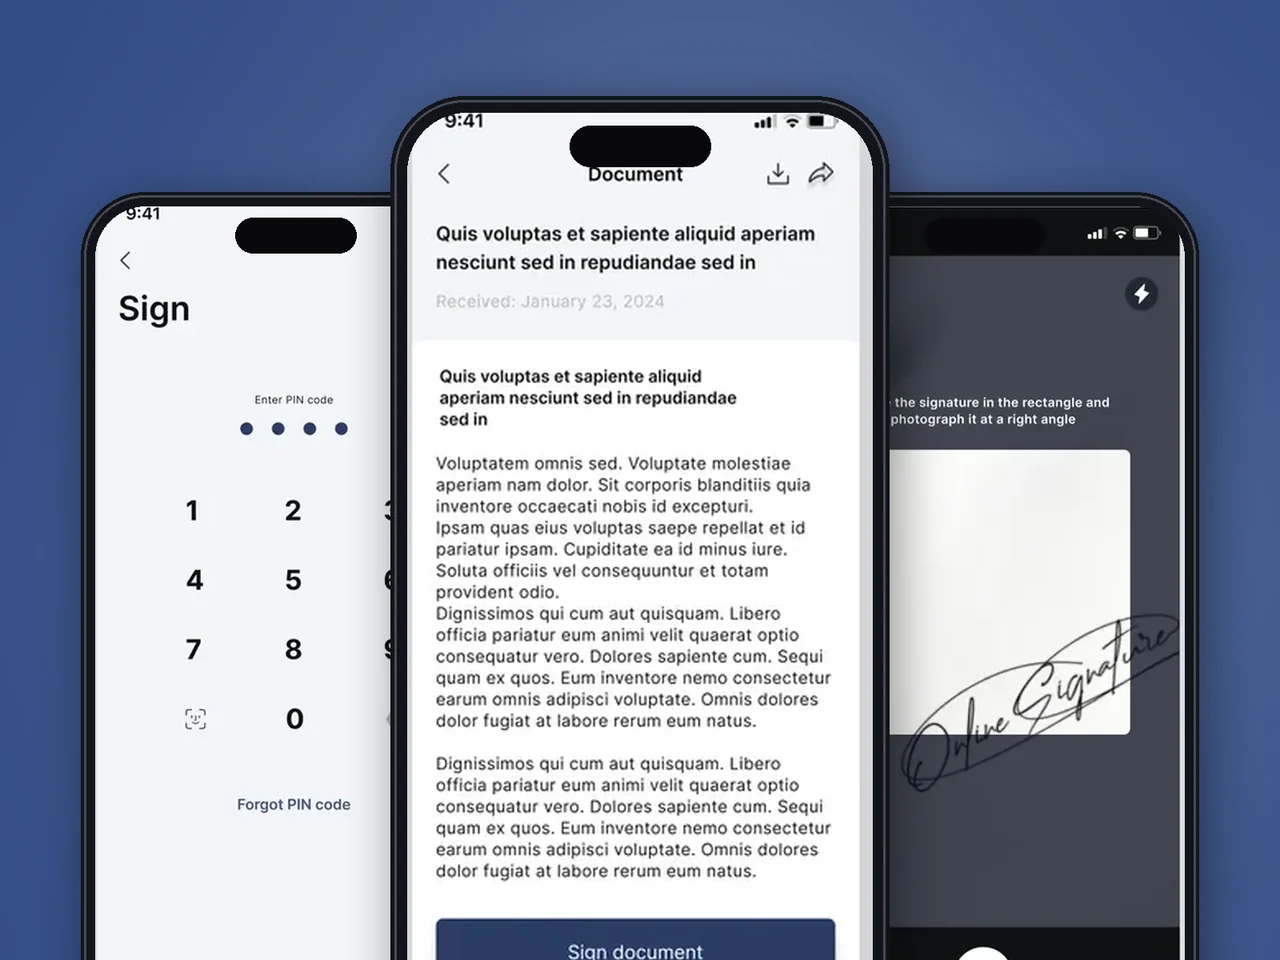
Native iOS and Android e-signature clients with a Symfony + React CRM for a cross-border law firm — KYC onboarding and a defensible evidence trail for US & EU matters.
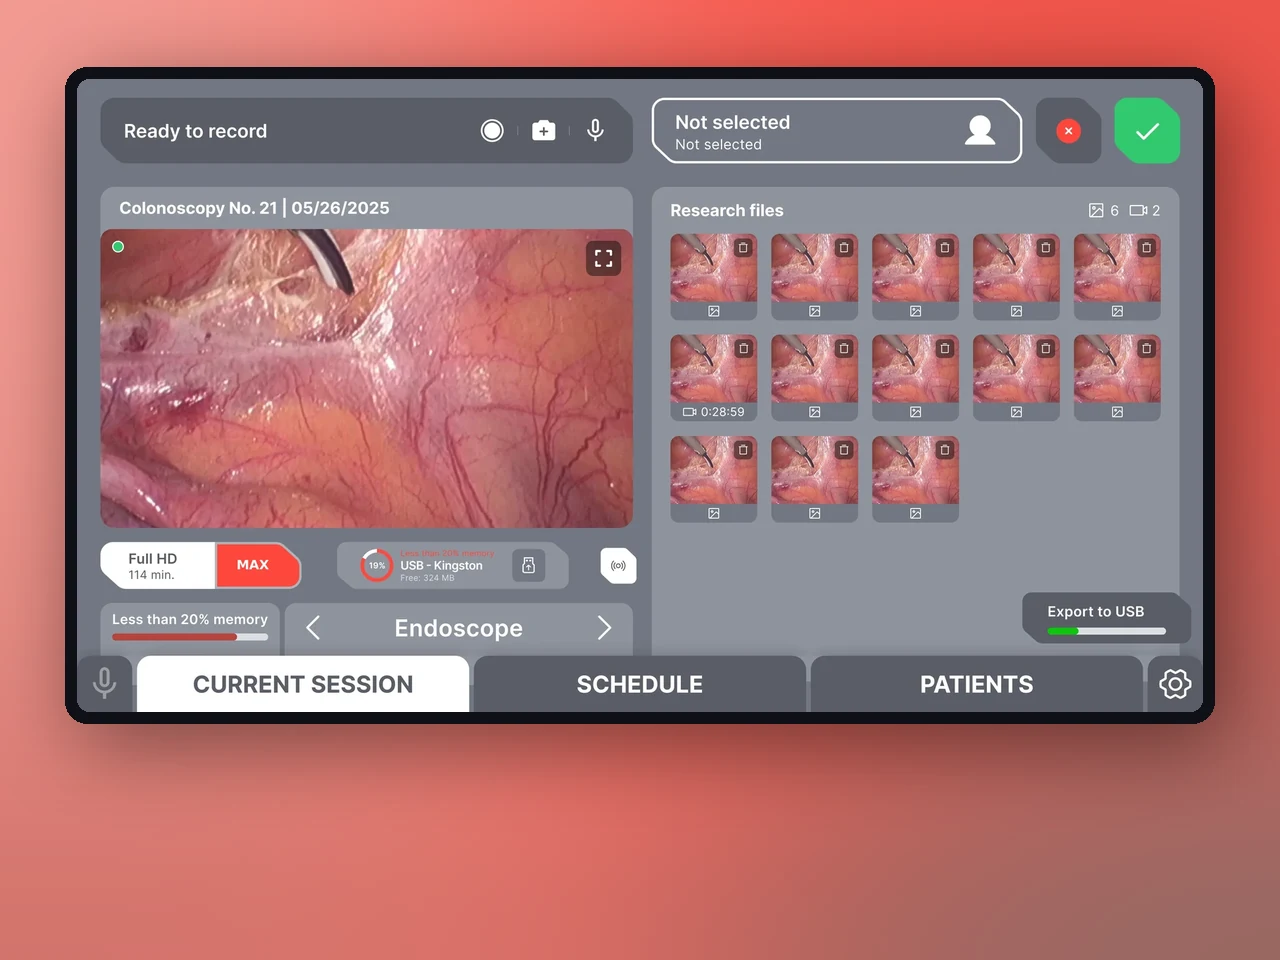
Tablet-first endoscopy recording, patient records, and DICOM/HL7 export — built on Laravel + React with browser-tier WebRTC capture for US & EU clinics.
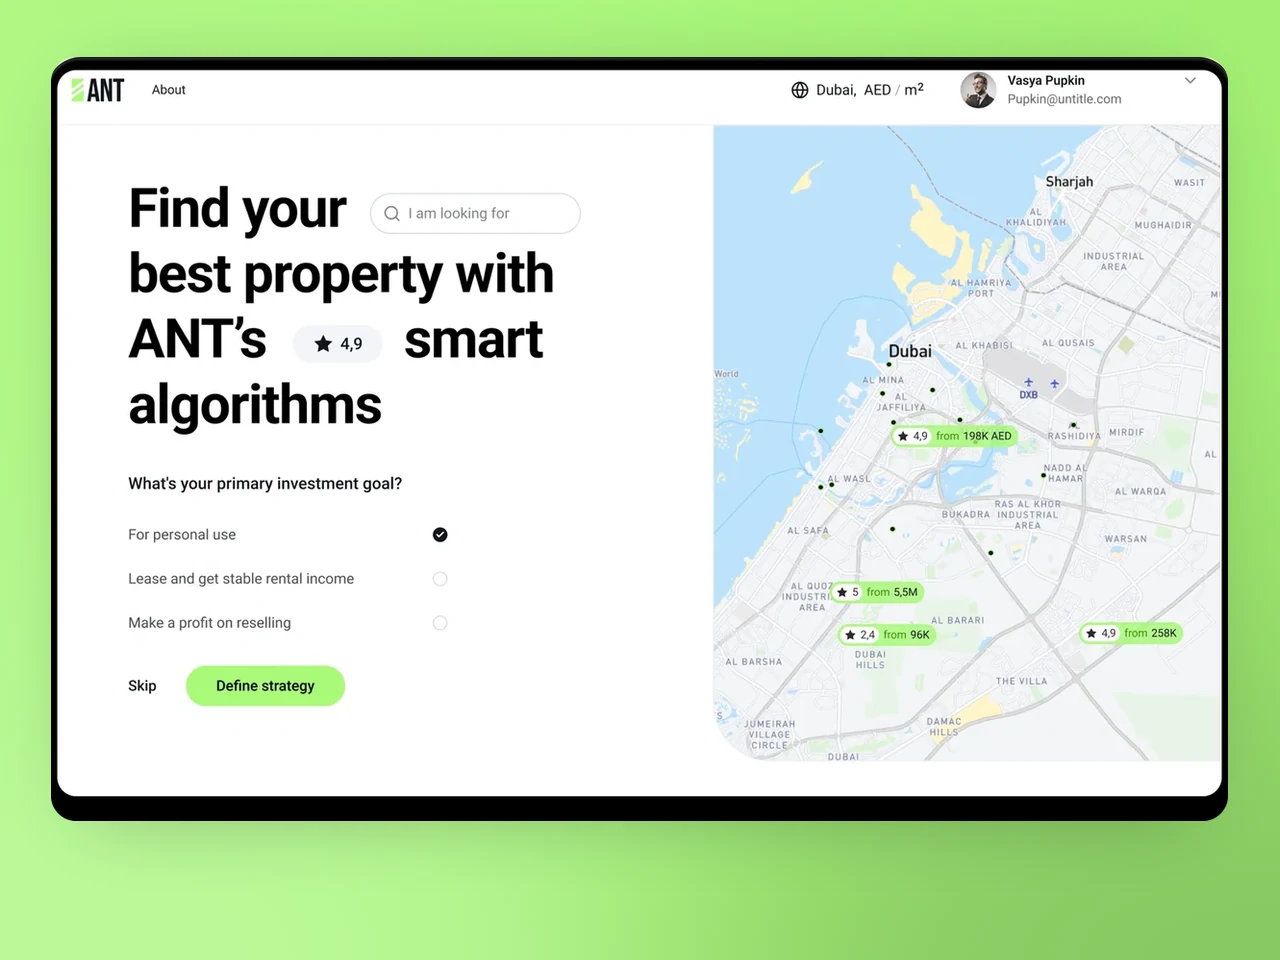
Property marketplace web platform with listing CMS, search and B2B admin console for US and EU operators.
Remote document signing is a legal minefield. YuSMP built both the mobile signing flow and the Symfony CRM in a single engagement, handled KYC onboarding, and delivered API docs that our compliance team cleared in days.
Clinical workflow software that hospitals actually adopt is rare. YuSMP built an iPad-first endoscopy platform with HD video capture, DICOM export, and HL7 integration. Medical staff needed almost no training because the UX is genuinely intuitive.
A loan decision engine that takes ten times less time to approve does not happen by accident. YuSMP built the scoring pipeline, integration with credit bureaus, and a back-office that our underwriters actually enjoy using. Approval turnaround went from two days to under four hours.
We publish dozens of sports articles a day. YuSMP built an editorial pipeline using a Telegram bot as the CMS — editors post once, content lands on web, iOS, and Android instantly. The architecture requires zero daily maintenance.
1 / 4
We start every project with strict: true and no-explicit-any enforced. Type safety is a delivery requirement, not a style preference.
React front-ends, NestJS backends, React Native apps — all typed end-to-end with shared type packages or tRPC. No contract drift across the stack.
OpenAPI → TypeScript client generation wired into CI — frontend types update automatically when the API spec changes.
FAQ
Monorepo with a shared types package (Turborepo or Nx) for manual type definitions, or OpenAPI codegen (openapi-typescript or orval) to generate TypeScript clients from your API spec automatically. tRPC for teams that want end-to-end type safety without a schema intermediate. The right choice depends on whether you control both ends of the API contract.
Yes, but incrementally. Enable strict: true with ts-ignore-count suppression tracking — measure the suppression count per PR and require it to decrease or stay flat. Never increase it. Typically 8–16 weeks to zero suppressions on a mid-size codebase with deliberate effort.
Zod is our default for new TypeScript projects — runtime validation, TypeScript inference from schema, excellent error messages, works in browser and Node. class-validator for NestJS applications where decorator-based validation integrates cleanly with the framework. io-ts for functional programming teams using fp-ts who want category-theory-aligned codecs.
type-coverage npm package reports the percentage of typed expressions per file. We gate on a minimum coverage threshold (typically 95%+) in CI and block PRs that reduce coverage. Combined with strict mode and no-explicit-any ESLint rule, this creates a ratchet — coverage can only improve.
tRPC for full-stack TypeScript monorepos where both client and server are in TypeScript and you want instant type safety without code generation. OpenAPI for projects with multiple consumers (mobile apps, third-party integrations), language-heterogeneous stacks, or existing API contracts you must maintain.
Project references (tsconfig references) for incremental builds — only changed packages rebuild. Turborepo or Nx for build orchestration with remote caching. A root tsconfig.base.json with strict settings that all packages extend. Package boundaries enforced with eslint-plugin-import or Nx constraints.
Tell us where you want to be in twelve months. We’ll come back with a plan to get you there.
Response within 1 business day. NDA on request.
Share a few details and a senior consultant will reply within one business day.
Email: sales@yusmpgroup.com
Phone: +374 44 871 811
Offices: KAMAR Business Center, Vazgen Sargsyan St. 2, Yerevan, Armenia · Remote — East-Coast US overlap (9 AM–1 PM ET)