N+1 query performance
Naive Django ORM usage generates N+1 queries on related objects. We use select_related, prefetch_related and annotate systematically, with query-count assertions in the test suite.
Django's batteries-included architecture — ORM, admin, auth, migrations, forms — lets teams ship production-grade Python applications without reinventing infrastructure. We build Django monoliths, Django REST Framework APIs and hybrid Django + React setups for US and EU clients, with a focus on multi-tenancy, role-based auth and GDPR-compliant data handling.
Django's batteries-included architecture — ORM, admin, auth, migrations, forms — lets teams ship production-grade Python applications without reinventing infrastructure. We build Django monoliths, Django REST Framework APIs and hybrid Django + React setups for US and EU clients, with a focus on multi-tenancy, role-based auth and GDPR-compliant data handling.
Naive Django ORM usage generates N+1 queries on related objects. We use select_related, prefetch_related and annotate systematically, with query-count assertions in the test suite.
Shared-schema multi-tenancy risks cross-tenant data leakage via ORM queries. We implement row-level security in PostgreSQL combined with Django middleware that scopes every queryset to the current tenant.
Django admin is powerful but often over-exposed. We restrict admin to internal VPN, add MFA, limit model permissions to the minimum required and audit all admin actions.
Fire-and-forget Celery tasks lose work on pod restart and mask errors silently. We configure task acks_late, retry with exponential backoff, dead-letter queues and Sentry integration for every task class.
Concurrent Django migrations in feature branches cause migration tree conflicts that block deployment. We enforce linear migration history via pre-push hooks and a squash protocol for release branches.
Deleting a user in Django leaves orphaned related objects and audit-log references. We implement cascaded anonymisation (not deletion) that satisfies erasure requests while preserving aggregated analytics.
Full DRF API with serializer validation, ViewSets, nested routers, throttling and token/JWT auth — OpenAPI schema generated via drf-spectacular.
Shared-schema multi-tenancy with PostgreSQL RLS and Django middleware — every queryset is tenant-scoped with zero risk of cross-tenant leakage.
Hardened admin panel with per-model permissions, custom list displays, inline editing, import/export and full audit log — ready for ops teams.
Celery workers with Redis broker — priority queues, retry policies, dead-letter queues, progress reporting and Sentry error capture.
pytest-django test suite with factory_boy fixtures, coverage enforcement, flake8/ruff linting and database migration smoke tests in GitHub Actions.
Access, rectification and erasure request views backed by cascaded anonymisation — documented and tested against GDPR Article 17 requirements.
GDPR-aligned · Django auth audit · HIPAA data isolation · SOC 2 logging
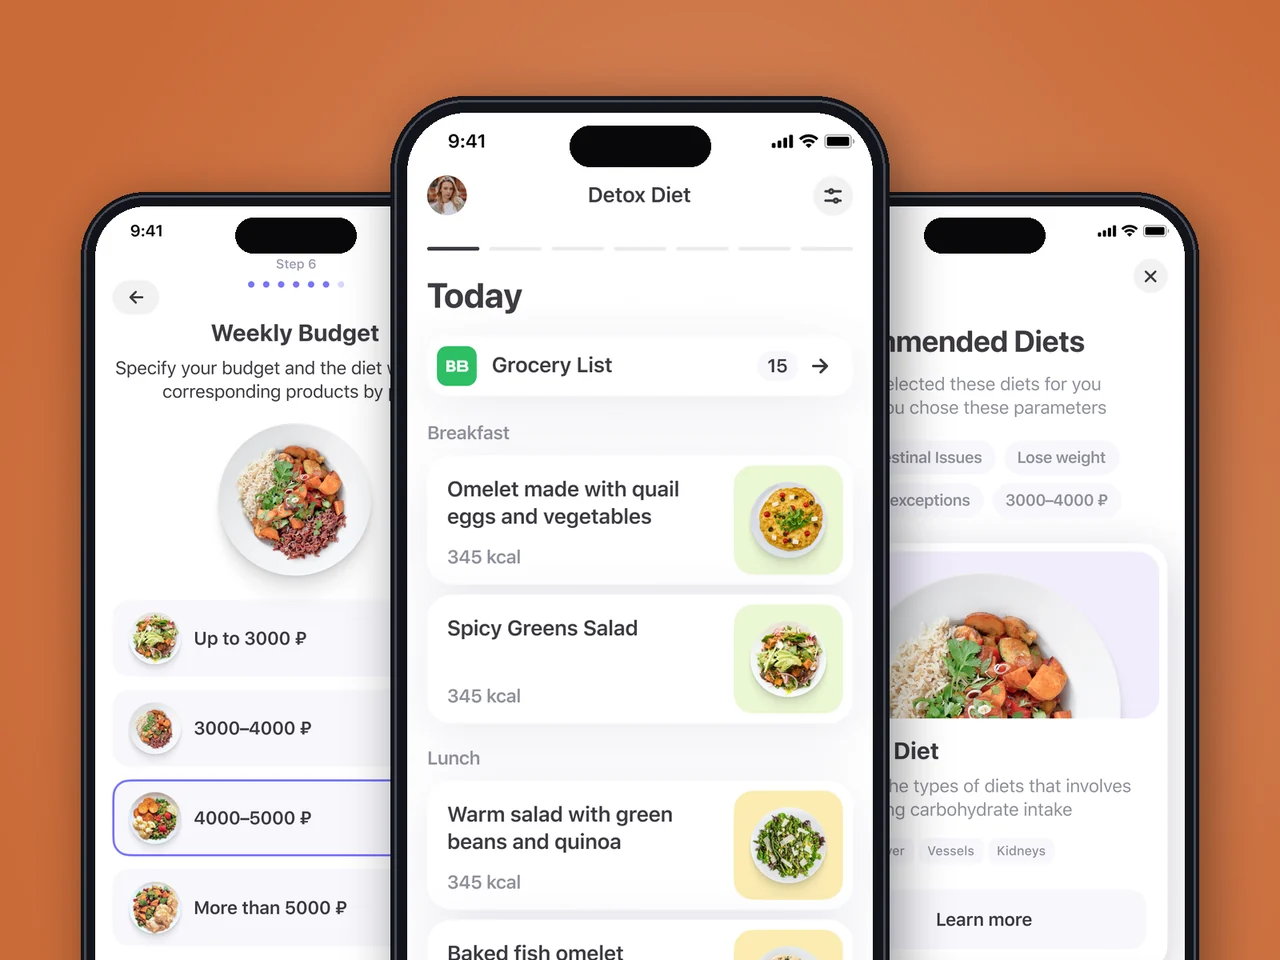
Cross-platform diet and meal-planning app on Flutter — calorie engine, recipe library, weekly meal-plan, grocery ordering.
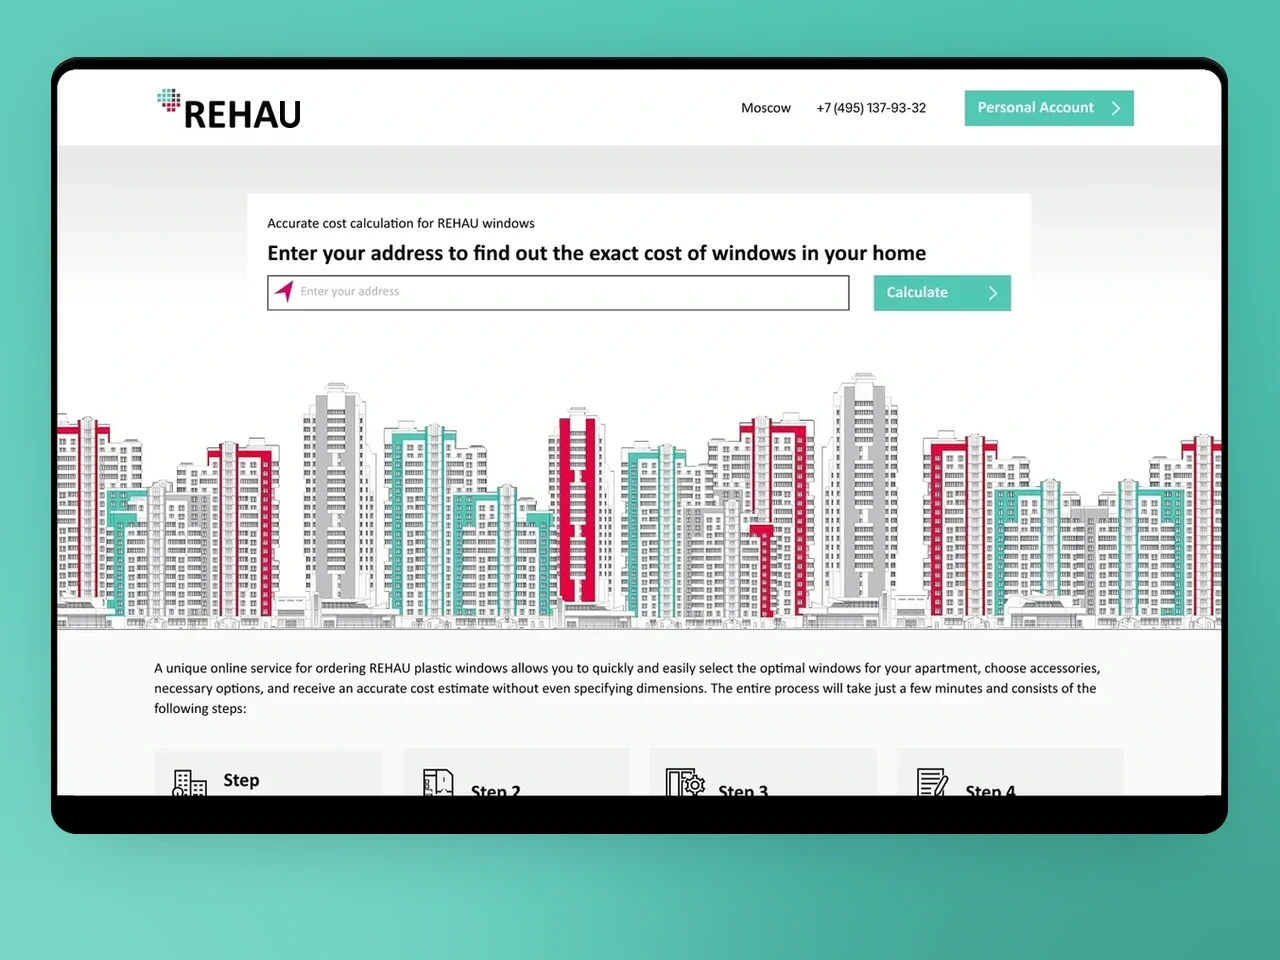
B2B e-commerce and product configurator for a global polymer manufacturer with multi-region pricing, stock and dealer workflows.
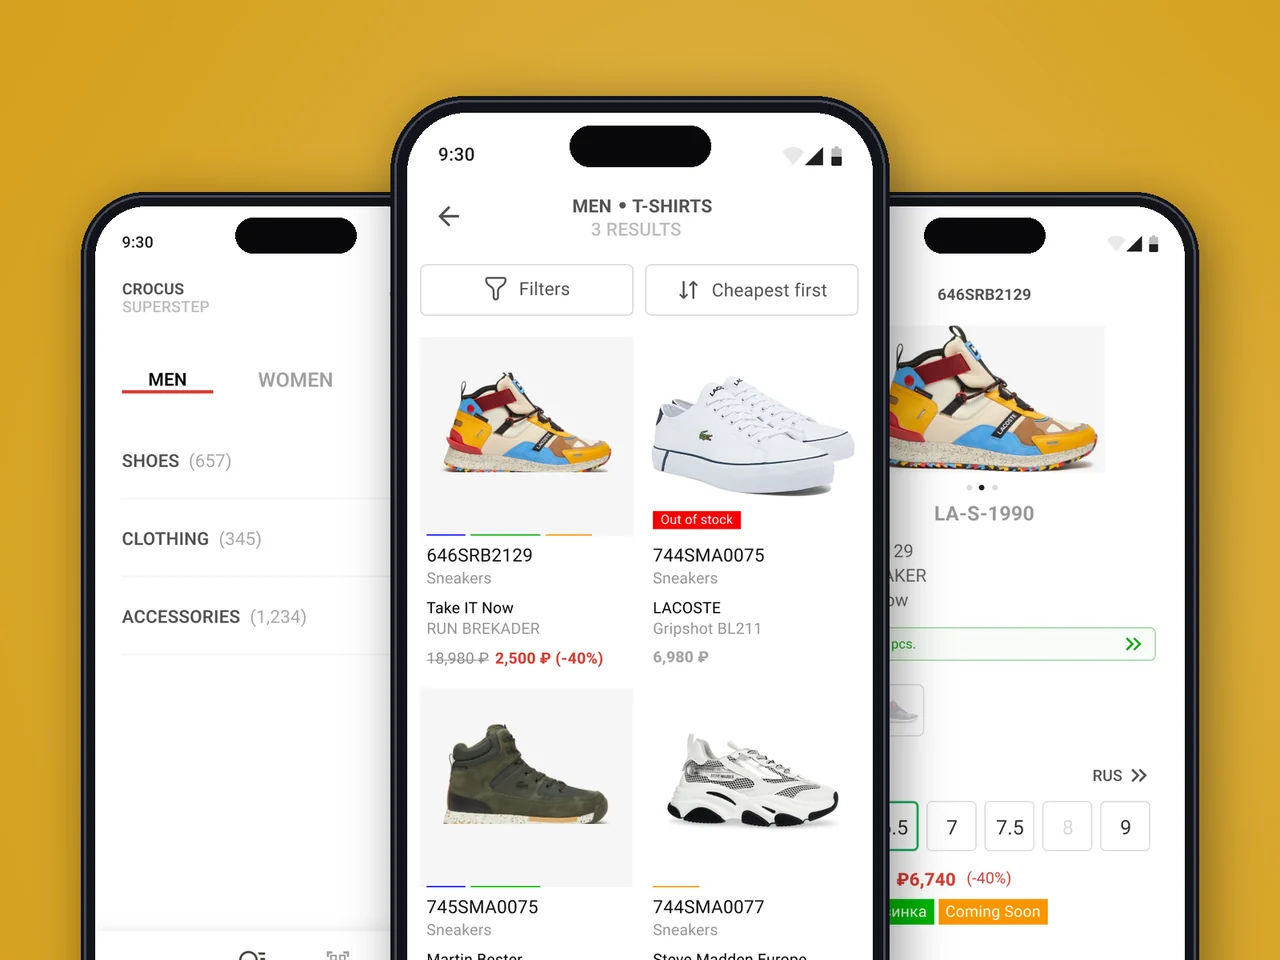
Retail POS companion app for a multi-brand boutique chain — ElasticSearch cross-store inventory search, 1C-system integration.
Our consultants were losing 15 minutes per customer on manual inventory checks. YuSMP built native apps backed by ElasticSearch, wired to our 1C system in real time. Time-per-customer dropped 40% across all locations within a week of launch.
We had a concept and tight timelines. YuSMP converted a Flutter skeleton into a production-ready nutrition app with a calorie engine, meal plans, and App Store subscriptions in four months. 90-day retention exceeded our benchmark by 30%.
B2B commerce for a polymer products brand means complex product configurators, dealer pricing tiers, and order workflows that non-technical buyers must navigate. YuSMP built a platform our dealers adopted without a single training session. Order volumes through the portal doubled in year one.
A loan decision engine that takes ten times less time to approve does not happen by accident. YuSMP built the scoring pipeline, integration with credit bureaus, and a back-office that our underwriters actually enjoy using. Approval turnaround went from two days to under four hours.
1 / 4
Django's ORM, admin panel, auth system and migrations eliminate months of boilerplate — we focus engineering time on your business logic, not infrastructure.
CSRF protection, clickjacking prevention, SQL injection resistance and XSS escaping are built in. We enforce SECURE_SSL_REDIRECT, HSTS and Content Security Policy on top.
Django monoliths can be decomposed gradually — we design the initial data model and API surface to support future service extraction without a full rewrite.
FAQ
Django when you need an ORM, admin panel, auth system and full-stack templating included — typical for internal tools, content platforms, e-commerce backends and multi-tenant SaaS. FastAPI when you need native async, auto-generated OpenAPI docs and Pydantic validation — typical for microservices and ML inference APIs. Many systems use both: Django for the admin/CMS layer, FastAPI for the high-throughput API surface.
DRF adds serialiser classes (input validation + output serialisation), ViewSets (CRUD endpoint generation), router-based URL configuration, throttling, pagination, filtering and built-in token/JWT authentication. It generates an OpenAPI schema via drf-spectacular. Plain Django views are sufficient for rendered templates; DRF is the standard for API-first Django services.
We separate migration runs from application deployment. Migrations run in a pre-deploy job (Kubernetes init container or CI step) against the production database before the new app pods start. We test backward compatibility — the old app version must run against the new schema during rolling deployment. Destructive column changes use a multi-step migration sequence.
Yes, with the right stack. Gunicorn with multiple workers handles synchronous concurrency. For truly async workloads we use Django 4.1+ async views with ASGI (Uvicorn/Daphne). Celery handles CPU-bound and I/O-bound background work. At high scale, Django services sit behind a load balancer with read replicas and Redis caching for frequent queries.
We implement cascaded anonymisation rather than hard deletion. The user record is anonymised (email hashed, PII fields nulled), related content is anonymised or deleted per retention policy, and a separate audit record confirms the erasure. Aggregated analytics and audit logs (which may be legally required) are preserved without PII. The erasure endpoint is exposed via a DRF view authenticated by the user's own token.
Yes. Django Channels extends Django with ASGI, enabling WebSocket connections, long-polling and server-sent events. We deploy Channels with a Redis channel layer for horizontal scaling. Use cases include real-time notifications, collaborative editing, live dashboards and chat.
We restrict the admin to an internal VPN or IP allowlist, enable MFA via django-otp, limit each user to the minimum required model permissions, add an audit log for every admin action via django-simple-history, and monitor login attempts with fail2ban. ADMIN_URL is changed from /admin/ to a non-guessable path.
Tell us where you want to be in twelve months. We’ll come back with a plan to get you there.
Response within 1 business day. NDA on request.
Share a few details and a senior consultant will reply within one business day.
Email: sales@yusmpgroup.com
Phone: +374 44 871 811
Offices: KAMAR Business Center, Vazgen Sargsyan St. 2, Yerevan, Armenia · Remote — East-Coast US overlap (9 AM–1 PM ET)